
Date, Time, and Location
Wednesday, September 23, 2026, 10:25 a.m. – 11:10 a.m.
Commonwealth Room, 50 Washington Street, Westborough
Session Description
This session covers how cyber-attacks arrive and what staff are expected to do when one reaches them. We open with the threat landscape and why employee accounts are a primary entry point, and what an attacker gains from a single compromised login. The core of the session is phishing: the impersonation and baiting tactics behind it, the indicators that give a message away, and exactly how to report one you're unsure about. We will also cover AI deepfakes and social engineering; synthetic voice and video used to impersonate colleagues and leadership, and the pretexting and urgency patterns underneath them. The session closes with handling sensitive data, the need-to-know access, securing screens and documents, and how to report a suspected incident.
Participation in this module will satisfy participant’s mandatory 2027 cyber security training requirement.
Session Documentation
Speaker Bios
Brad Smith
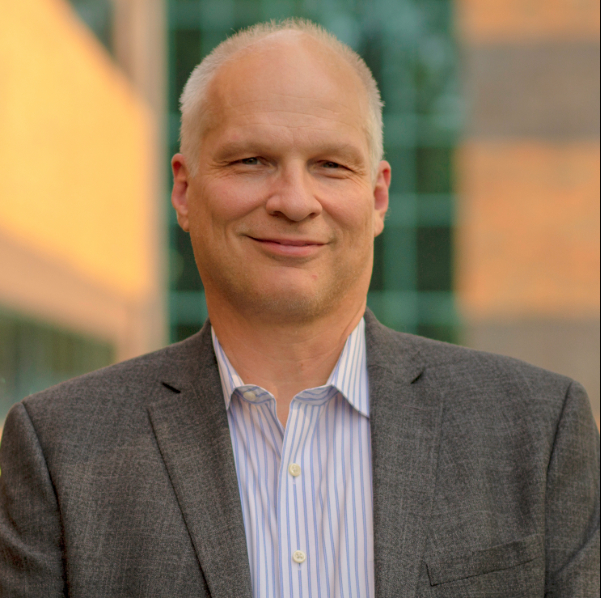
Brad Smith serves as the Chief Information Security Officer for the UMass President’s Office. He has worked for the University since May of 2018. His prior positions include:
- Technology and Management Consultant for the Commonwealth of Massachusetts, AARP, New England Power
- Professional Services Consultant Digital Equipment Corporation.
Iris Lyons
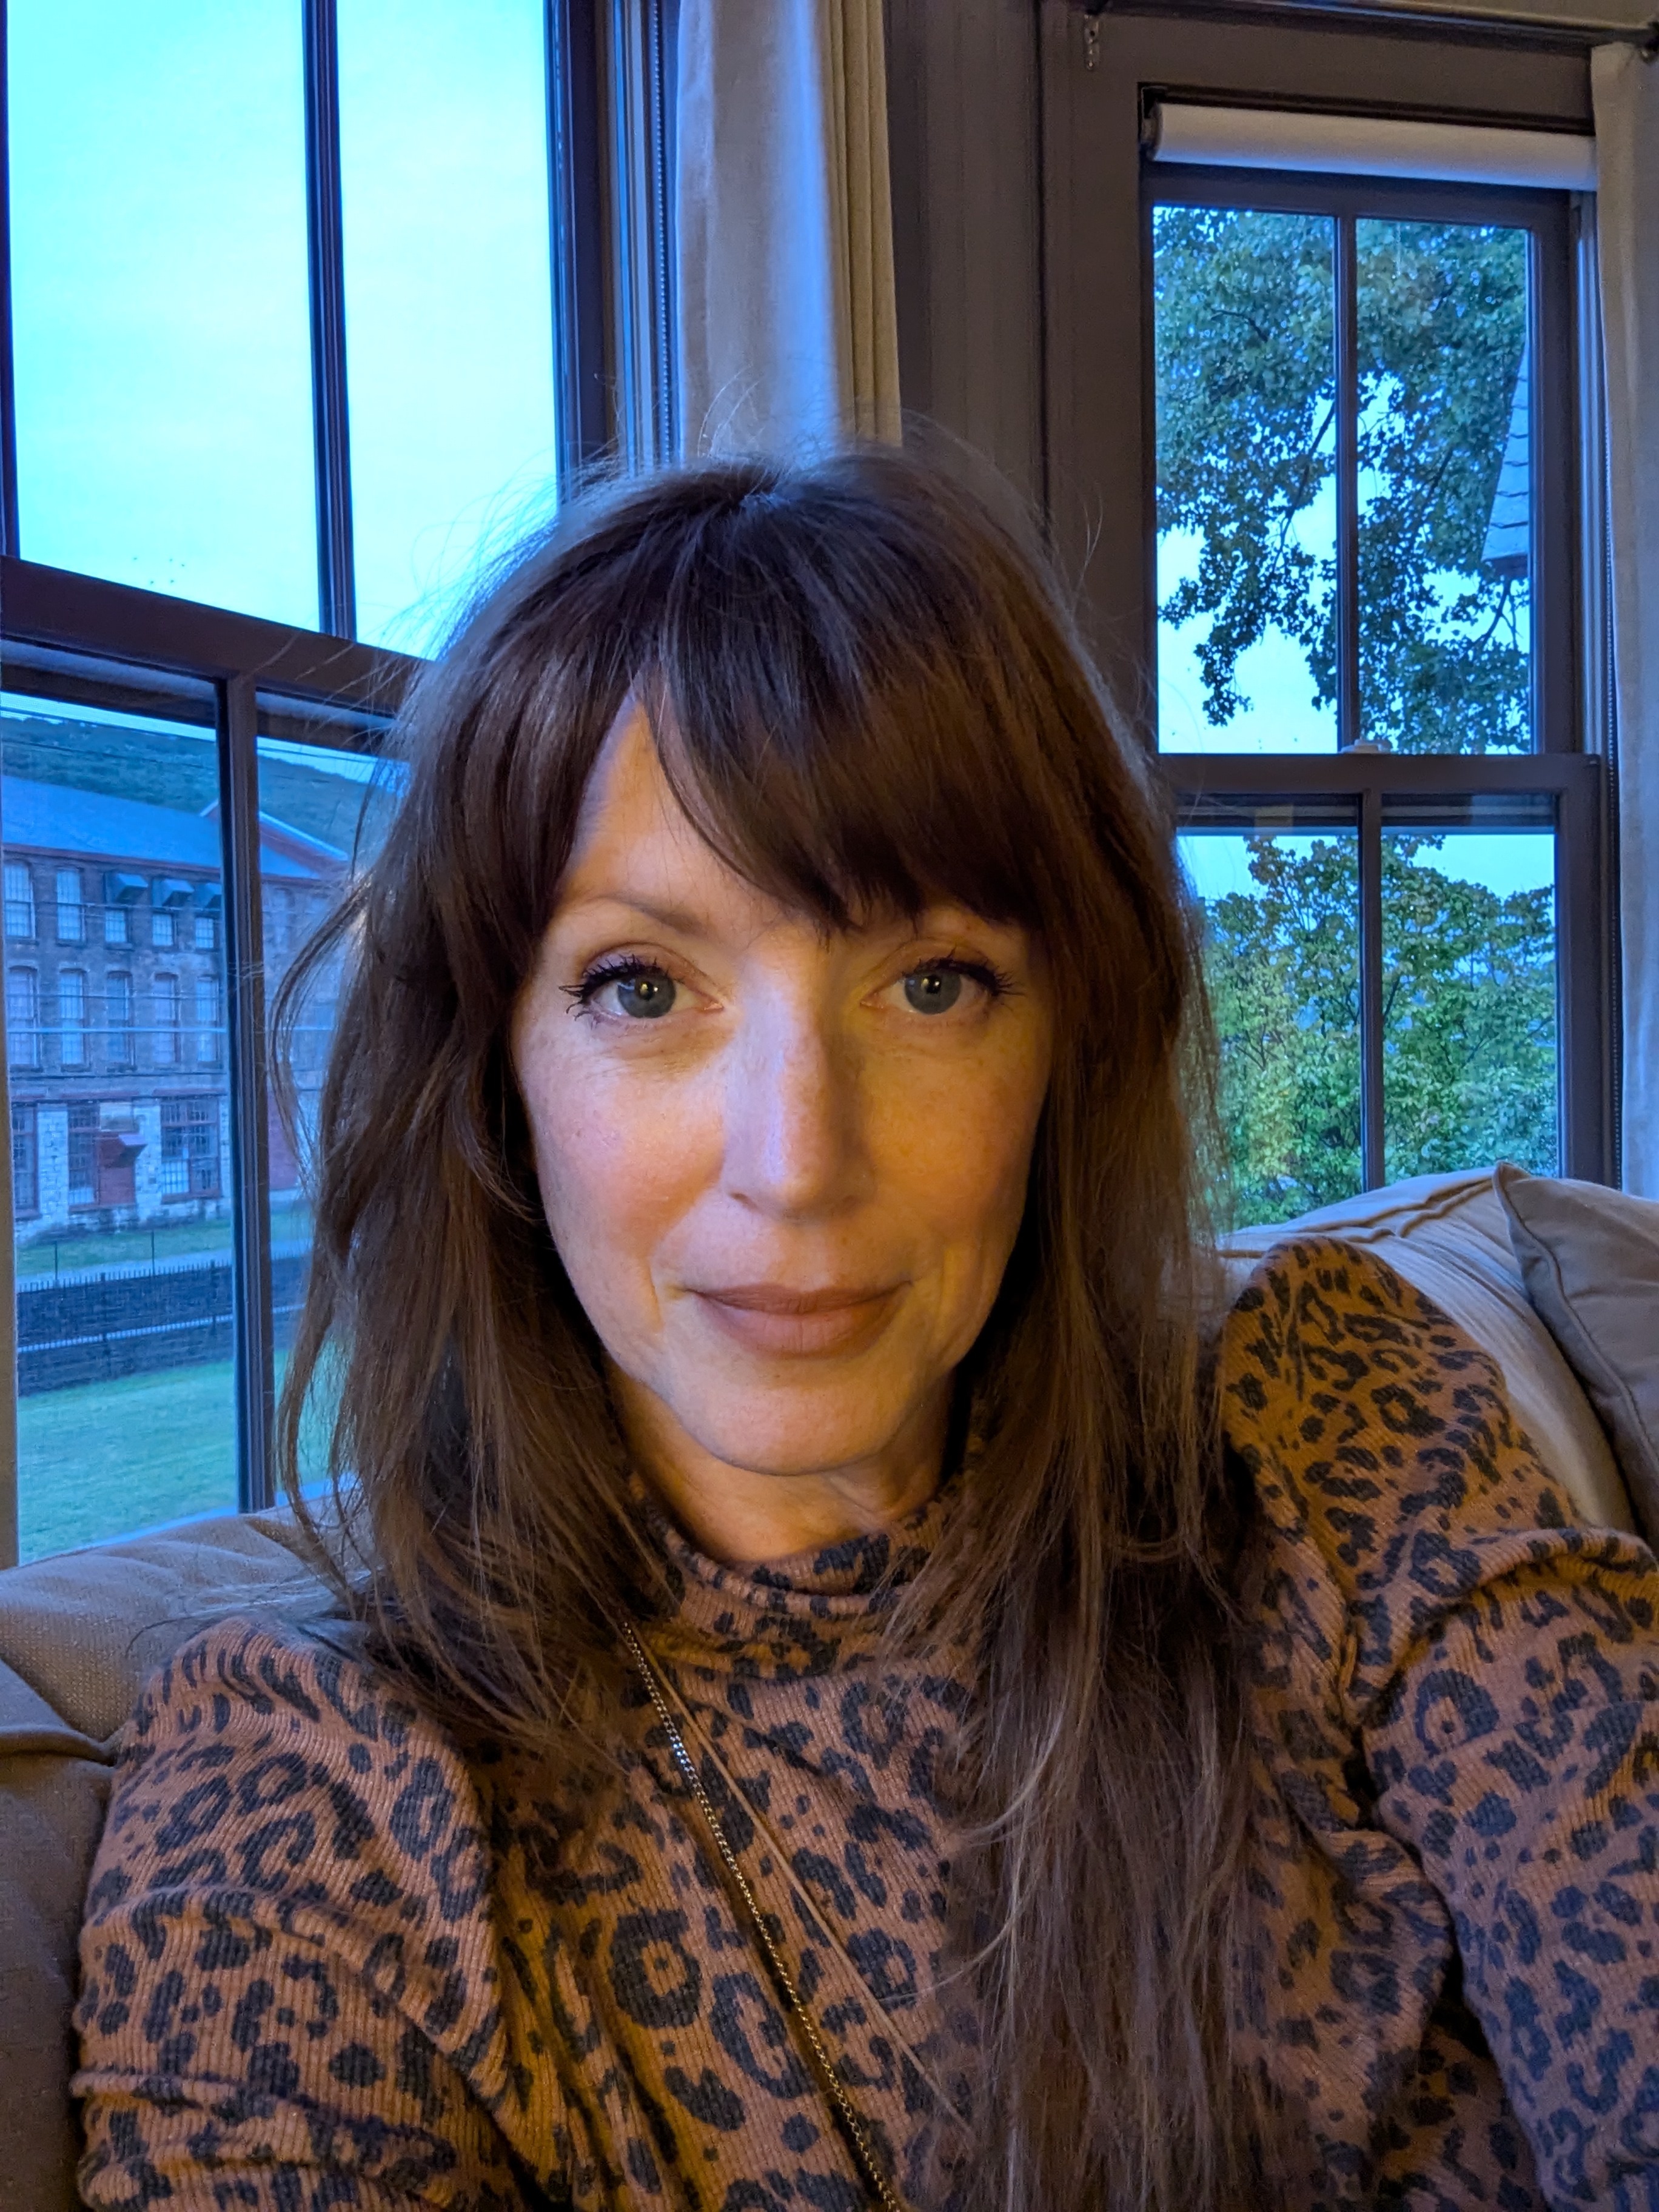
Iris Lyons is the Information Security and Disaster Recovery Lead at the UMass President’s Office. She started at UMPO in 2013 but after a brief hiatus returned in 2023 to the best office in the organization. Her prior positions include:
- Service Delivery Manager at Modo Labs
- Senior Project Manager at Hanover Insurance Company
- Senior Project Manager at UMPO
Iris holds a bachelor’s degree from MCLA and is a member of ISACA.
View Full Day 1 Agenda
Return to the Day 1 Agenda.